Why is Sysmon event ID 2, "a process changed a file creation time", a useful detection signal?
Because legitimate software almost never rewrites a file's creation date, while attackers do it on purpose (timestomping) to make a freshly dropped file look old and blend in with the system files around it.
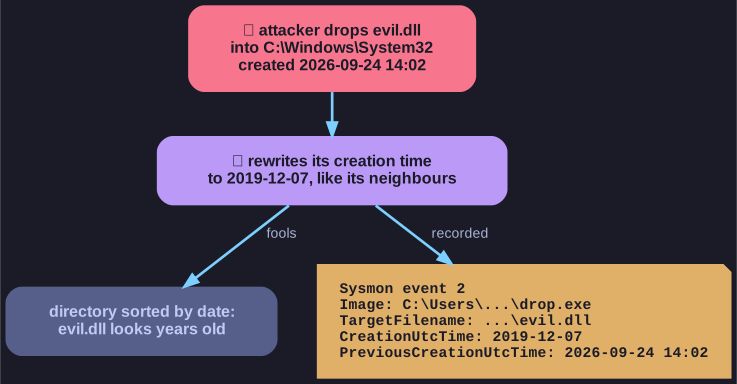
* The trick that hides the file from a directory listing leaves both timestamps in the log. *
Investigators often start by asking "what was created around the time of the incident?" and sort a directory by creation time. An attacker who drops evil.dll into C:\Windows\System32 and then sets its creation date to match the neighbouring files from years ago escapes exactly that search.
Sysmon event 2 records the process that changed the time, the file, and both the new and the previous creation time. So the trick that hides the file from a directory listing leaves a precise trail in the log instead. Installers and some sync tools do change timestamps legitimately, so the typical filter is: only files in user-writable paths, or executables, which is exactly what the example configuration rule for this event does.
Go deeper:
 MITRE ATT&CK T1070.006 — Timestomp — the technique, real-world uses and detection notes.