Where is an email gateway positioned, how do the firewall rules support it, and what changes with email-gateway-as-a-service?
It must be placed so that it can reach the mail exchangers on the internet, and the firewall allows email only between the gateway and the internet (gw <-> internet: allow email) while denying direct traffic between internet and company (internet <-> company: deny all). As a service, the gateway runs at a cloud provider, and the firewall then only allows email between the internal mail server and the cloud email service.
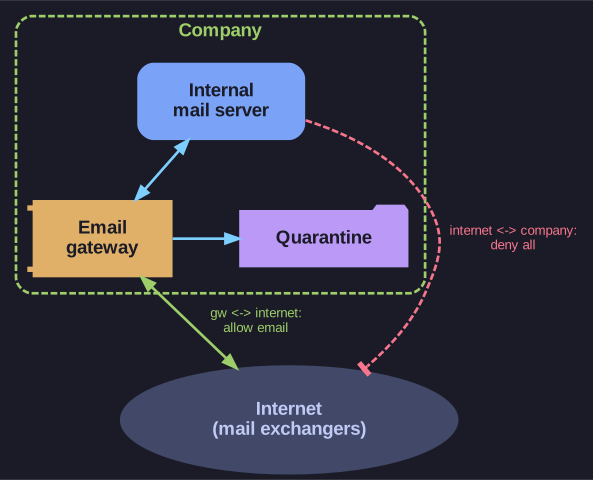
* The firewall rules leave the gateway as the only path for mail, so every message is inspected. *
The firewall rules are what force all email through the gateway: the internal mail server is not allowed to talk to the internet directly, so the only route for mail in or out is through the inspection point. A mail exchanger is the server that receives email for a domain, found through the DNS MX record.
With the cloud variant, the inspection moves out of the company and is rented as an integrated mail service. The principle stays the same: one path, and that path is the inspected one.
Go deeper:
 MX record — Wikipedia — how mail finds the server that receives it for a domain.
- NIST SP 800-45 Version 2 — Guidelines on Electronic Mail Security — securing mail servers, gateways and content filtering.