Question
Why are network firewalls alone not enough at the perimeter, and what is the idea behind adding gateways?
Answer
Attackers quickly move onto the communication the firewall allows: addresses are easy to fake, and attacks travel through permitted protocols and ports. Gateways answer this with smarter tools specialised in one protocol or kind of communication, which inspect much deeper. They sit as a passage in the perimeter, and all traffic they should control is rerouted through them.
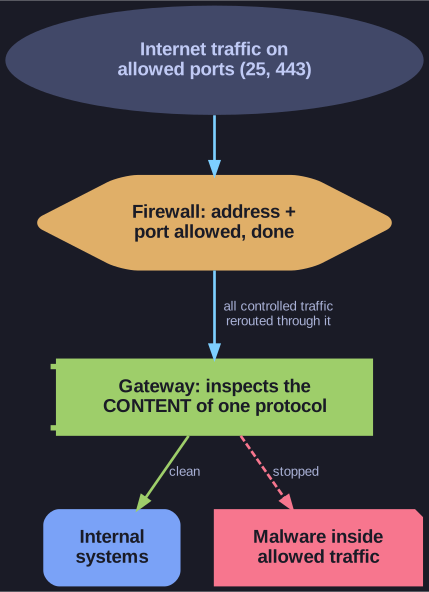
* The firewall only sees that port 25 or 443 is allowed; the gateway behind it looks at what actually travels through. *
A network firewall decides on combinations of address, protocol and port: some are allowed, everything else is denied. That is a coarse check. Once port 25 (email) or 443 (web) is open, the firewall has no idea whether what flows through is a business email or a malware attachment, a normal web page or a manipulated one.
A gateway (a "smart security tool") supports enforcing the perimeter by looking at the content of one specific kind of traffic. It only works if the traffic really goes through it: the firewall is set up so that, for example, only the email gateway may talk email to the internet, and nobody else.
Go deeper:
 Firewall (computing) — Wikipedia — packet filters, stateful and application firewalls side by side.
- MITRE ATT&CK T1071 — Application Layer Protocol — attackers hiding command traffic inside allowed protocols such as HTTPS and DNS.
Note saved — thanks!
Question
What is a gateway, which gateways matter for cyber security architecture, and which typical ones exist?
Answer
A gateway is a handover point or passage that connects two systems. For security architecture, the ones that matter carry an extra control function: email gateways, web proxies, data gateways and API gateways (each with content control), reverse proxies and application gateways.
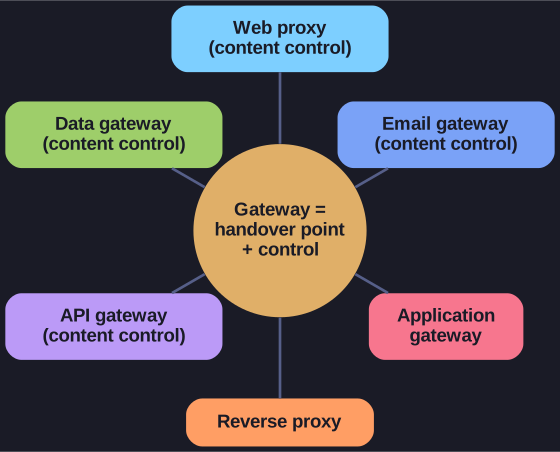
* Every one of these is a door in the perimeter that also inspects what passes. *
- Email gateway with content control: filters mail in and out.
- Web proxy with content control: filters web access from inside.
- Data gateway with content control: business data exchange with partners.
- API gateway with content control: publishes software interfaces to the outside.
- Reverse proxy: sits in front of servers and accepts requests on their behalf.
- Application gateway: a loosely used name, often a multi-function gateway.
A web application firewall belongs to the same family but is treated together with DMZ designs. The common thread: each one is a door in the perimeter that also inspects what passes.
Go deeper:
- Application-level gateway — Wikipedia — the narrower, protocol-specific meaning of the term.
- Proxy server — Wikipedia — forward and reverse proxies, the gateways that inspect what crosses.
Note saved — thanks!