Quiz Entry - updated: 2026.09.24
What is a subsearch in Splunk, and what does sourcetype=syslog [ search login error | return user ] do?
A subsearch is a search in square brackets that runs first and passes its result into the outer search as an argument; this one finds the user who last had a login error and then returns all syslog events of that user.
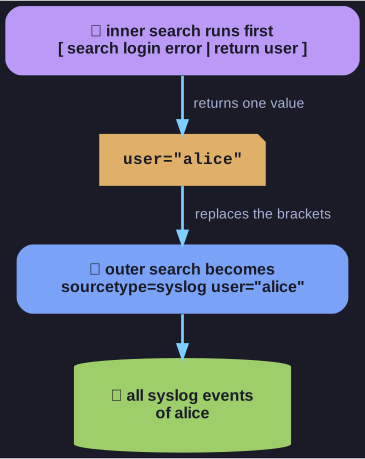
* Inner first, its result becomes the outer search's filter. *
Execution order:
- The inner search
search login error | return userruns on its own.return userhands back theuservalue of the first result, formatted asuser="alice". - That text replaces the bracketed part, so the outer search becomes
sourcetype=syslog user="alice". - The outer search runs normally.
return gives only one value by default; return 5 user returns up to five, combined with OR.
Subsearches are the SPL answer to "find X, then show me everything about X" without copying values by hand. They have limits (a default time and result cap), so for joining large data sets stats over both data sets is usually the better choice.
Go deeper:
 Splunk — About subsearches — execution order and the default result and time limits.