What does a Sysmon event ID 1 (Process Create) record, and which fields matter most for spotting an attack?
Everything about the new process and its parent: image path, command line, user, hashes, integrity level, and the parent's image and command line. The parent-child relationship and the command line are the most telling fields.
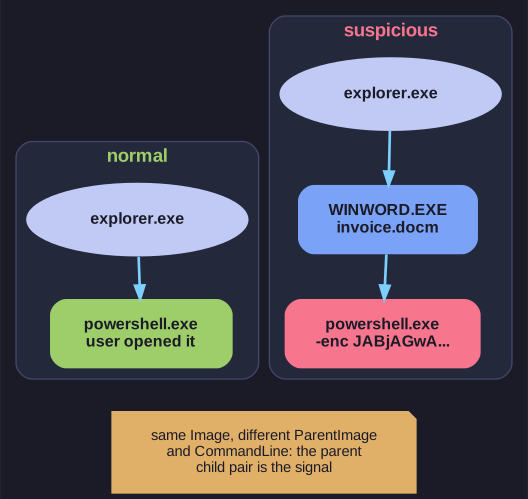
* Identical child image, different parent and command line: that pair is the signal. *
Key fields:
| Field | Meaning |
|---|---|
Image |
Path of the new (child) executable |
CommandLine |
Arguments it was started with |
User, IntegrityLevel |
Who ran it, with what privilege |
Hashes |
Hash(es) of the executable |
ParentImage, ParentCommandLine |
Which process started it, and how |
ProcessGuid, ParentProcessGuid |
Unique IDs to link events together |
OriginalFileName |
Name from the PE header, survives renaming |
Why the parent matters: powershell.exe on its own is normal. powershell.exe -enc JAB... (an encoded command) whose parent is WINWORD.EXE is a classic sign of a malicious Office macro. Likewise, a file called svchost.exe in C:\Users\...\AppData whose OriginalFileName says mimikatz.exe has been renamed to hide. Neither pattern is visible from the process name alone.
Go deeper:
 MITRE ATT&CK T1036.005 — Match Legitimate Name or Location — how attackers name malware after system binaries, and how to detect it.