Is Sysmon an antivirus, an application whitelisting tool or a host intrusion detection system?
None of them: Sysmon only records. It blocks nothing, raises no alerts and makes no verdicts; the detection happens afterwards, when someone or something analyses the logs.
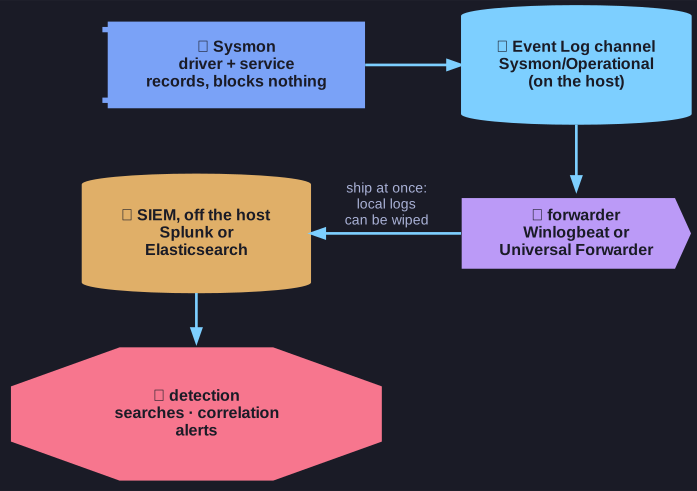
* Recording happens on the host; detection only after the events reach the SIEM. *
That is a common misunderstanding. Sysmon is an advanced logging service with built-in filtering. Its filters decide what gets written down, not what is allowed to run. (Newer versions add a few optional "file block" events, but its core purpose remains logging.)
The practical consequence is architectural. Sysmon's value appears only when its events leave the endpoint and land somewhere they can be searched, correlated and alerted on: a SIEM such as Splunk, or the Elastic Stack. An attacker with admin rights can also stop or reconfigure Sysmon (which is why event 4, service state changed, and event 16, configuration changed, are worth alerting on) and can wipe the local log, which is a second reason to forward events off the host immediately.
Go deeper:
 Security information and event management — Wikipedia — what a SIEM does with the events Sysmon records.