A company has both a CISO and an IT security manager. What is the division of labour between information security and IT security?
Information security asks what must be protected and why; IT security asks how to protect the IT landscape. The first supplies the content-side justification, the second implements it technically.
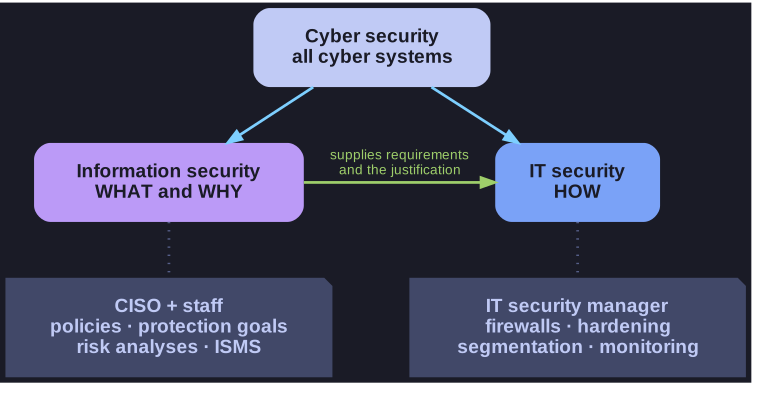
* Information security sets what and why; IT security builds the how — which is why the CISO usually sits outside IT. *
| Information security | IT security | |
|---|---|---|
| Central question | What do I protect, and why? | How do I protect an IT landscape? |
| Concerned with | The protection needs of the information being processed | Technical protective measures |
| Typical role | CISO — Chief Information Security Officer — and their staff | IT security manager, IT security admins, security operations |
| Typical home | Its own organisational unit, deliberately outside IT | Inside the IT department |
| Typical output | Security policies, protection goals, risk analyses, an ISMS | Firewalls, hardening, segmentation, tooling, monitoring |
The dependency runs one way: information security delivers the factual, content-side basis for the measures that IT security builds. Without it, technical security becomes taste — you cannot say whether a control is adequate if nobody has said what the asset is worth and which risk is tolerable.
The separation is also a deliberate conflict-of-interest design. IT is measured on availability, cost and delivery speed; if the person who says "this risk is unacceptable" reports to the person under pressure to ship, the verdict bends. That is why the CISO frequently sits outside IT.
In smaller companies the two jobs are routinely merged into a single "security manager" — which is workable, but note what has been lost: the same person now sets the requirement and grades their own homework.
Both sit under the umbrella of cyber security, whose remit is securing cyber systems in general.
Go deeper:
 Wikipedia — Chief Information Security Officer — the reporting-line debate in numbers: putting the CISO under the CIO is treated as a conflict of interest.