Question
What does cyber security architecture do that buying individual security products does not?
Answer
It is the discipline of the whole construction: which building blocks are chosen, how they are wired together, and which processes run around them — for one defined stretch of a cyber system.
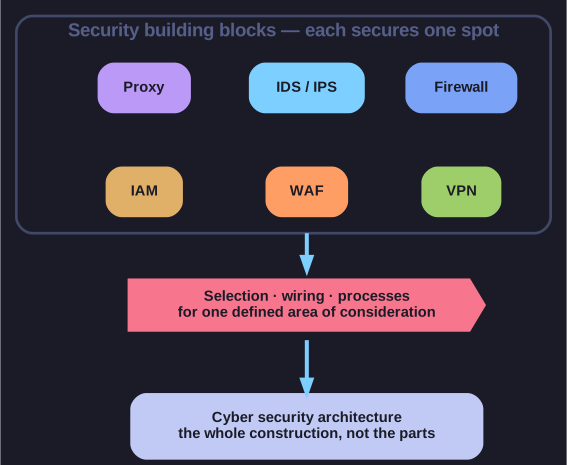
* Products are the materials; the architecture is the plan that selects, wires and operates them for one defined area. *
The security market sells parts, not buildings. Network security secures networks, an intrusion detection system acts as a burglar alarm, a virus scanner keeps malware off a host, a web application firewall filters HTTP traffic, an IAM system decides who may log in. Each product secures one spot or one aspect, and each is perfectly capable of being correct in isolation while the estate around it stays wide open.
Architecture is the level above that. It answers three questions that no single product answers:
- Selection — which blocks does this estate actually need? (An expensive product that guards a door nobody uses buys nothing.)
- Wiring (Verschaltung) — how do they connect, what does traffic have to pass, where are the boundaries and the control points?
- Processes — who patches, who reviews the rules, who grants access, what happens on an alert? A firewall whose rule set nobody prunes decays into a router.
And crucially it applies to a defined area of consideration (Betrachtungsraum) — a system, a site, a company, an estate — because "secure" is only meaningful once you have said what is being secured and where it ends.
The building analogy holds up well: bricks, pipes, steel and glass are the materials; a house is what happens when someone decides which ones, in what arrangement, for which purpose. Products are materials. Architecture is the plan.
Go deeper:
 Wikipedia — Enterprise information security architecture — the established frameworks (SABSA, TOGAF, Zachman) that formalise exactly this planning layer.
Note saved — thanks!
Question
Why is there no single authoritative definition of "cyber security architecture", and what should you do about that in practice?
Answer
Neither half of the term is standardised — "cyber security" and "architecture" are both practitioner words shaped by usage, not by one international standard — so you work from common usage and, in a real conversation, pin down what the other side means.
There is no ISO or IEEE clause that fixes the term the way, say, ISO/IEC 27001 fixes what an ISMS is. Both components are loose:
- "Cyber security" is used in a narrow sense as a straight synonym for IT security, and in a wider sense — the one that makes the discipline interesting — as the security of all cyber systems, industrial control and embedded devices included.
- "Architecture" is borrowed from building and reused across IT and its neighbouring disciplines (enterprise architecture, solution architecture, software architecture, security architecture), each with its own tradition of what an "architecture" deliverable actually is.
The practical consequences are real rather than academic:
- Two people can agree to "improve the cyber security architecture" and mean completely different deliverables — a network diagram, a target-state paper, a set of policies, or a rebuild programme.
- Job adverts for "security architect" describe wildly different jobs.
- When you read a document, the author's definition governs; when you write one, define your terms early.
Tip: treat it like the word "platform". Everybody uses it, nobody means quite the same thing, and the cheap fix is one sentence of definition at the top of your document.
Go deeper:
- NIST glossary — "security architecture" — NIST itself lists four different definitions from four documents — the ambiguity in one screen.
Note saved — thanks!