Quiz Entry - updated: 2026.09.17
Which topologies of IAM systems are distinguished?
Isolated (local) identities; central identities or identity federation in the variants RP-centred, IdP-centred, full mesh and hub-and-spoke; and provisioning.
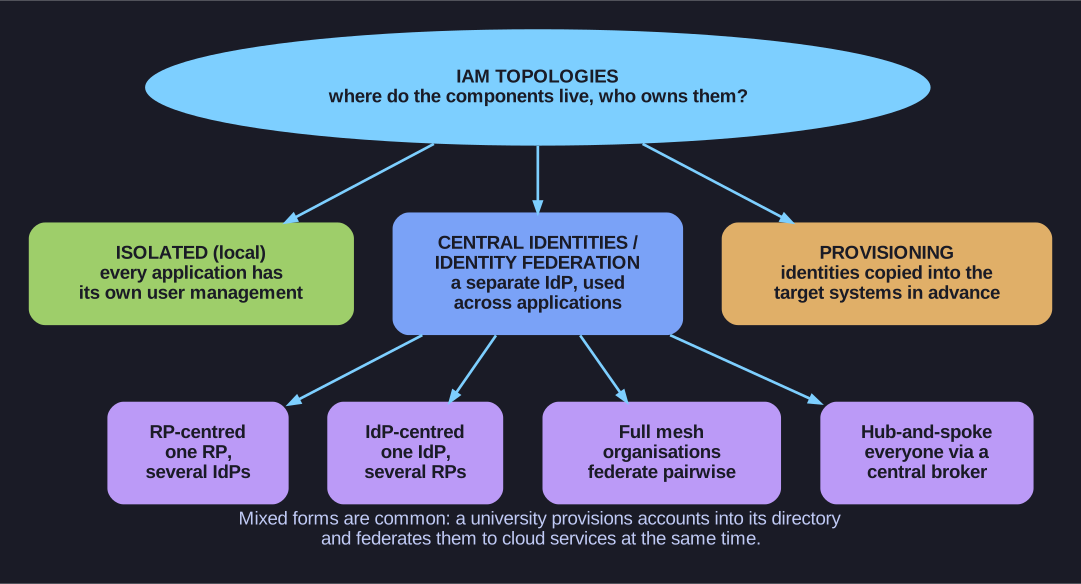
* The topology families: isolated, central or federated in four layouts, and provisioning. *
The topology says where the IAM components live and who owns them:
- Isolated (local) identities: every application has its own built-in user management.
- Central identities / identity federation: identities are issued by a separate identity provider and used across applications. Four layouts exist for how IdPs and relying parties are wired together:
- RP-centred: one relying party accepts several IdPs.
- IdP-centred: one IdP serves several relying parties.
- Full mesh: several organisations federate with each other.
- Hub-and-spoke: everyone talks through a central broker.
- Provisioning: identities are copied from a source into the target systems in advance rather than being asserted at login.
Mixed forms are common in practice; a university, for example, provisions accounts into its directory and federates them to cloud services at the same time.
Go deeper:
 Federated identity (Wikipedia) — how identities and attributes are linked across separately managed systems.