Quiz Entry - updated: 2026.10.20
Which measures make up the on-premises security architecture for the print shop?
① Replace the FTP server with a modern HTTPS data-exchange solution. ② Add content control and file-type checks to the HTTPS gateway. ③ Use an email gateway with content control and route all email through it. ④ Set up a DMZ for the gateways. ⑤ Restrict the usable protocols with firewalls. ⑥ Segment the LAN further with firewalls.
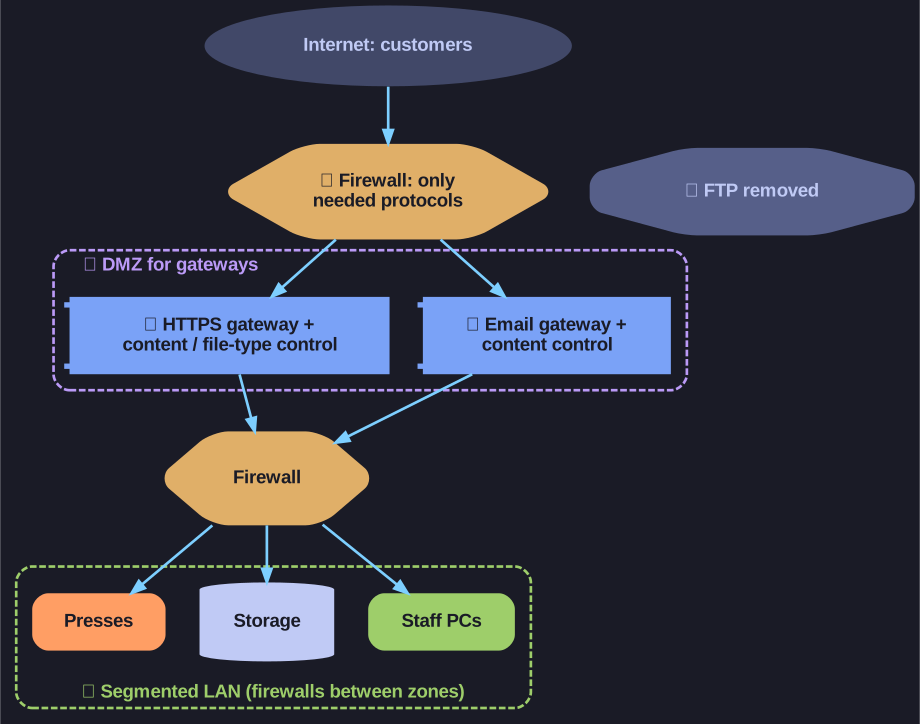
* Fewer openings, each remaining one inspected, gateways in a DMZ, and zones inside to contain an infection. *
- Remove FTP. FTP is old and unencrypted, and its function is covered by the HTTPS gateway, so it is dismantled rather than secured.
- Content and file-type control on the upload gateway, so only expected types (PDF, InDesign, CSV) get in, and they are checked.
- Email gateway with content control and file-type checks, with all mail forced through it.
- DMZ for the gateways: the internet-facing mail server and upload gateway move into their own zone, so a compromised gateway is not inside the office network.
- Firewalls limit the protocols that may cross at all.
- Further segmentation of the LAN: printing presses, data storage and staff PCs in separate zones, so ransomware on one PC cannot reach the presses.
The design fits the small budget: fewer openings (FTP removed, no VPN), each remaining one controlled, and zones inside so one infection stays contained.
Go deeper:
 DMZ (computing) — Wikipedia — single- and dual-firewall DMZ designs.
- Content Disarm and Reconstruction — Wikipedia — rebuilding incoming files without their active content, a strong form of content control.
- NCSC — Mitigating malware and ransomware attacks — the defences, including filtering and segmentation, in one guide.