When do the CRA's obligations apply, and which standards will support it?
Reporting of actively exploited vulnerabilities and severe incidents applies from 11 September 2026. All other requirements apply from 11 December 2027. 41 harmonised standards are being developed: horizontal ones (the EN 40000-1 series) and vertical ones per product group.
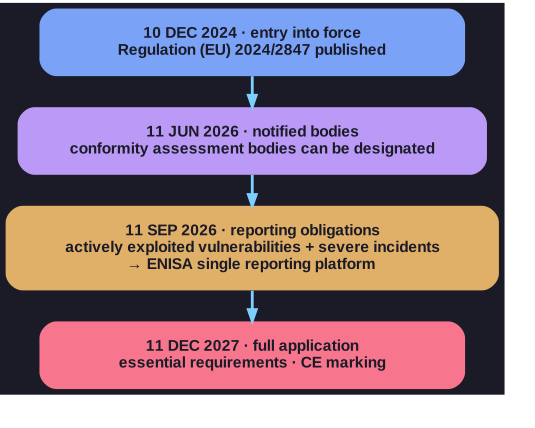
* Reporting came first; the essential requirements and CE marking follow in December 2027. *
Timeline:
- 11 September 2026: reporting obligations for actively exploited vulnerabilities and severe incidents.
- 11 December 2027: all requirements, including the essential requirements and CE marking.
Harmonised standards turn the CRA's general essential requirements into concrete, testable ones. A product that follows them is presumed to conform. That is what lets Important class I products use self-assessment.
- Horizontal (all products, EN 40000-1 series): vocabulary, principles of cyber resilience, vulnerability handling, generic security requirements.
- Vertical (per product group): network components (routers, switches, firewalls, VPNs), software products (browsers, password managers, operating systems, hypervisors), smart-home and consumer products (locks, cameras, wearables, toys), industrial components (microcontrollers, ASICs, FPGAs, smart meter gateways) and security components (HSMs, smartcards, secure elements).
The EU also publishes an official FAQ, guidance for manufacturers and a self-assessment tool.
Go deeper:
 European Commission — CRA implementation FAQ — dates, harmonised standards and transitional rules
 Cyberstand — CRA self-assessment tool — check whether and how the CRA applies to a product