What security activities belong to each stage of a typical DevSecOps pipeline?
Plan: test plan, test cases, hardening spec, release policies. Code: linter or IDE checks, unit tests, SCA. Build: SAST, compiler flags, package updates, hardening. Test: DAST, integration tests. Release: pentest, approval for prod. Deploy: update the configuration database, set up monitoring.
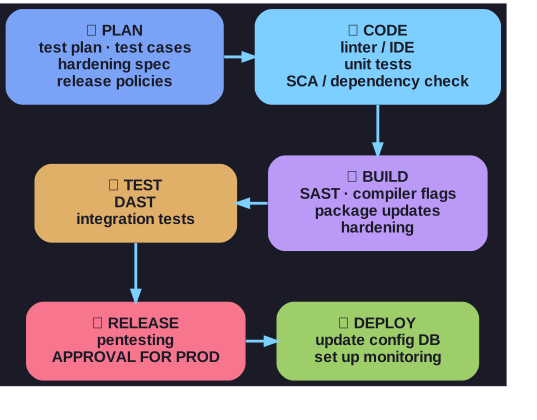
* Each check sits where its input first exists; approval for prod is the gate before deploy. *
| Stage | Security activities |
|---|---|
| Plan | Security test plan, security test cases, hardening specification, release policies |
| Code | Linter or IDE checks, unit tests, SCA and dependency check |
| Build | SAST, security compiler flags (stack protection, PIE), package updates, hardening |
| Test | DAST, integration test cases |
| Release | Pentesting, approval for prod |
| Deploy | Update the configuration database, set up monitoring |
Each check sits where its input first exists. SAST needs code, DAST needs something running, and a pentest needs a release candidate. The deploy stage feeds the post-launch loop. The configuration database records exactly what was deployed, which vulnerability management later compares against new CVEs.
Go deeper:
 OWASP DevSecOps Guideline — which tool class to put in which pipeline step