What is the goal of the security planning and classification phase, what are its steps, and what typically goes wrong?
Classify how critical the product is, which tells you the applicable laws and target security level, then plan the activities, time and resources to reach it.
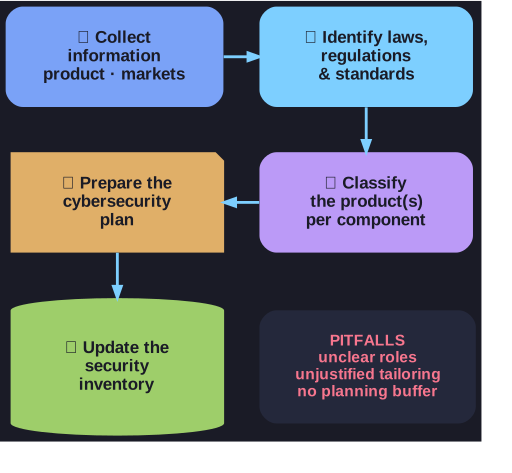
* Five steps from product information to an updated security inventory, and the three classic pitfalls. *
Classification comes first because everything after it scales with it. A smart toaster and a hardware security module need very different amounts of testing and certification, and the classification tells you which one you are building. The five steps:
- Collect information about the product and its target markets.
- Identify laws, regulations and standards that apply in those markets.
- Classify the product(s), per component where it makes sense.
- Prepare the cybersecurity plan: activities, deliverables, roles, resources.
- Update the security inventory with the classified product.
It needs management commitment, a product description with target markets, a classification scheme and a product security inventory. Good practice is market-specific criticality indicators, a simple scheme, and tying the plan into the normal project plan. The typical failures are unclear roles, unjustified tailoring (skipping activities without a documented reason) and no buffer in the schedule for security work.
Go deeper:
 Cyberstand — CRA self-assessment tool — walks through whether the CRA applies and which category a product falls into