Quiz Entry - updated: 2026.10.15
What is the difference between HTTP 401 Unauthorized and 403 Forbidden?
401 means the server doesn't know who you are (missing or invalid authentication); 403 means it knows who you are, but you are not allowed to do this.
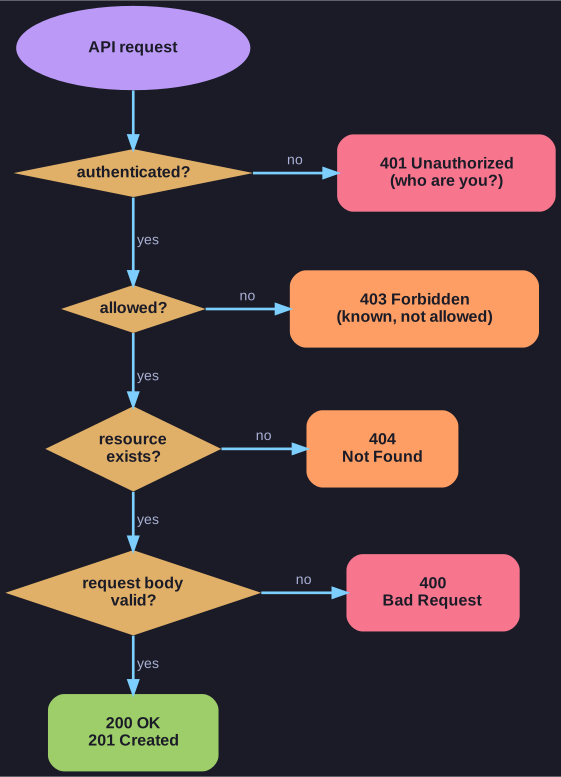
* A typical order of checks behind the status code; servers differ in the details. *
| 401 Unauthorized | 403 Forbidden | |
|---|---|---|
| Problem | Authentication: who are you? | Authorisation: are you allowed? |
| Typical cause | No token, expired token, wrong password | Valid account, but lacking the role or permission |
| Fix | Log in again or get a fresh token | Use an account with the right rights |
The name "Unauthorized" for 401 is a historical misnomer: it really means unauthenticated. With a controller API that uses tokens, a 401 halfway through a script usually means the token has expired.
Go deeper:
 401 Unauthorized — MDN — with the WWW-Authenticate challenge the server sends back.
- 403 Forbidden — MDN — when re-authenticating won't help.