What is security traceability, and why do almost all secure development standards require it?
An unbroken chain of links from product requirements through architecture, risk mitigations and technical requirements to test cases, results and reports. It proves each requirement was implemented and each mitigation works as specified.
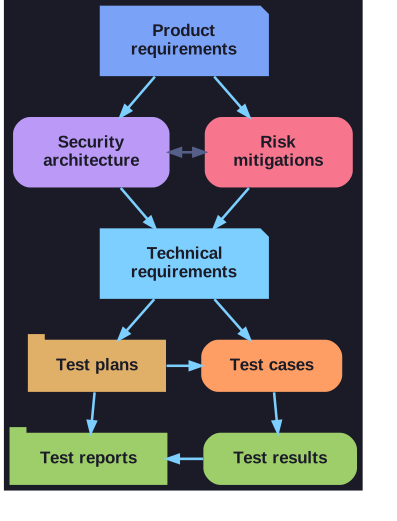
* Every test result traces back to a requirement or a risk mitigation, and every requirement forward to a test. *
The chain runs:
Product requirements → security architecture and risk mitigations → technical requirements → test plans and test cases → test results → test reports.
Following it forwards shows that every requirement has a test. Following it backwards shows that every test result goes back to a requirement or a mitigation. That is what an auditor or certification body asks for. Without it, "we tested security" cannot be shown for any particular requirement. Standards require it because it is good development practice. Tools range from Jama, SystemWeaver, Jira and HP ALM to plain Word and Excel.
Go deeper:
 Requirements traceability (Wikipedia) — forward and backward tracing explained
- Traceability matrix (Wikipedia) — the table format used in practice