What is Kerberos, and what does the KDC do in it?
Kerberos is a ticket-based network authentication protocol (based on Needham-Schroeder); the KDC (Key Distribution Center), which is the domain controller in AD, issues the tickets.
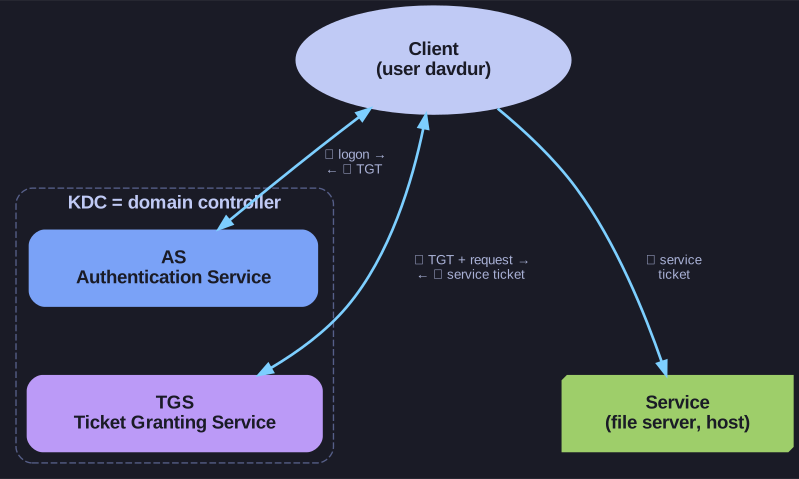
* One logon gets a TGT; each service ticket comes from the TGS; the service never contacts the KDC. *
The goal is secure, uniform authentication in a network with single sign-on: the password is used once at logon, and after that the user proves who they are with tickets. The password never travels over the network.
Three parties take part: the client that wants to log in, the service it wants to use, and the KDC, which all of them trust. The KDC has two parts:
- the Authentication Service (AS) checks the user at logon and issues a TGT (Ticket Granting Ticket),
- the Ticket Granting Service (TGS) takes the TGT and issues a service ticket for one specific service.
The flow:
- The client authenticates to the AS and gets a TGT.
- For each service, the client shows the TGT to the TGS and gets a service ticket.
- The client shows the service ticket to the service. The service can check it with its own key and never needs to contact the KDC.
The KDC is central because it holds the secret keys of every user and service. That is why domain controllers are the most valuable systems in an AD environment.
Go deeper:
 Computerphile: Taming Kerberos — the whole ticket exchange explained on paper.
 Varonis: Kerberos Authentication Explained — the AS, TGS and service steps with diagrams.
- Wikipedia: Kerberos (protocol) — history, the protocol in detail, and its weaknesses.