What is Common Criteria (ISO/IEC 15408), and how does a certification run?
A generic security certification scheme for IT products, hardware and software. It is often used for smartcards, HSMs, secure elements and other security devices. The product (the Target of Evaluation) is evaluated against a Security Target at an assurance level EAL 1 to 7, ending in a certificate from a national authority such as the BSI.
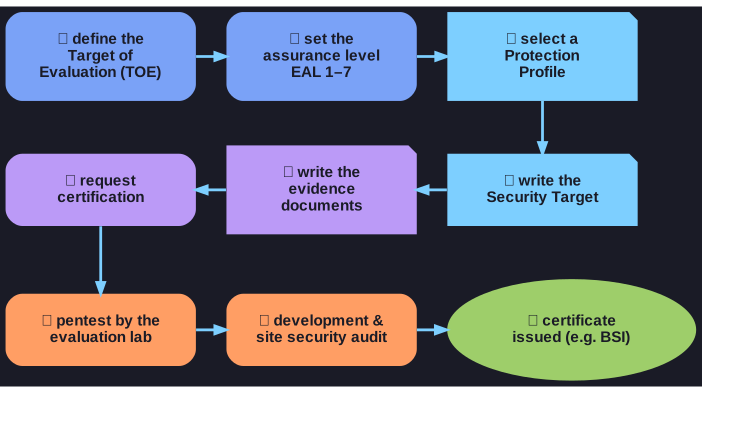
* From the Target of Evaluation to the certificate: the documents first, then the lab and the site audit. *
Common Criteria has three parts: 15408-1 terms and concepts, 15408-2 security functional requirements, 15408-3 assurance requirements. ISO 18045 (the CEM) is the evaluation method. It covers both product security and development security. For the development side, JIL's Minimum Site Security Requirements (MSSR) audit the development and manufacturing sites.
The certification steps:
- Define the scope: the Target of Evaluation (TOE).
- Define the target assurance level: EAL 1 to 7.
- Select a Protection Profile: the standard requirement set for that product type.
- Write the Security Target: the claims for this specific product.
- Write the evidence documents.
- Request certification.
- Product pentesting by an accredited evaluation lab.
- Development and site security audit.
- Certificate issued by the responsible authority, for example the BSI in Germany.
Tip: Protection Profile = requirements for a product type. Security Target = claims for your product.
Go deeper:
 Common Criteria portal — protection profiles and every certified product
- Common Criteria (Wikipedia) — EALs, protection profiles and security targets explained