What has to be prepared at "definition time" so that access control can work at runtime?
Before any runtime check is possible, the IAM system needs maintained digital images of subjects and resources, defined access rules, and the supporting processes for operation, support and governance.
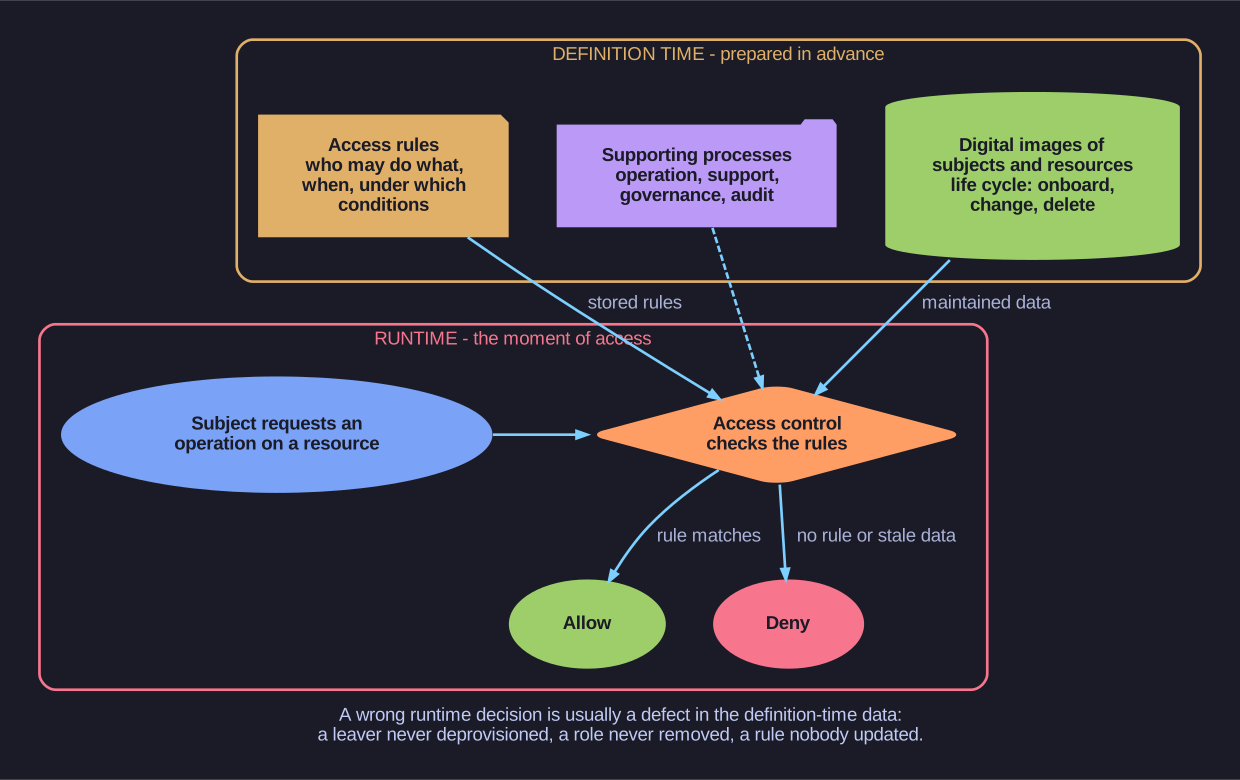
* The runtime check is the visible tip; the data and rules it relies on are prepared at definition time. *
Access control is the visible tip; almost all IAM work happens earlier, at definition time:
- Digital images of subjects and resources must exist and be kept current in the IAM system. This is where the life-cycle processes live: onboarding, mutations (changes) and finally deletion.
- Access rules must be defined: who may do what, when and under which conditions.
- Further processes are needed around the system: operating it, supporting users, governance, audit and so on.
The lesson is that a wrong runtime decision is usually not a bug in the access check but a defect in the data behind it: an employee who left but was never deprovisioned, a role that was never removed, a rule nobody updated. Good IAM is mostly good definition-time hygiene.