What does "Delegate Control" on an OU do, and why is it better than making the helpdesk domain admins?
It grants one group a specific, limited set of rights on the objects in one OU, for example "Reset Password" on user accounts, instead of full administrative power over the whole domain.
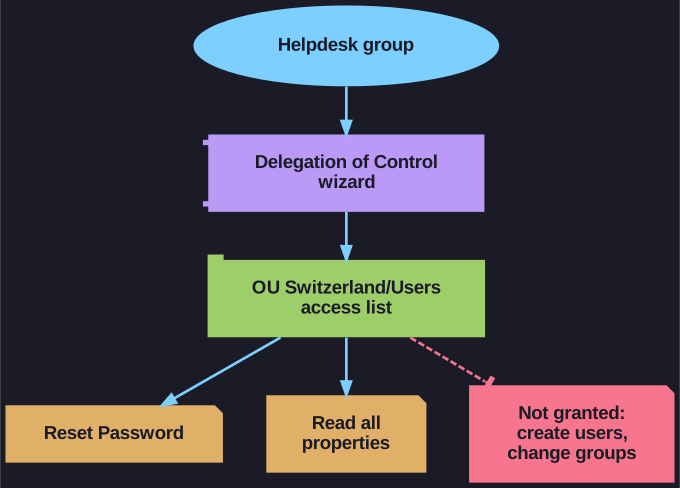
* The wizard writes two narrow entries on one OU and grants nothing else. *
The helpdesk's actual job is resetting forgotten passwords. The Delegation of Control wizard writes exactly the needed entries into the OU's access list. After delegating "Reset user passwords" to the helpdesk group on Switzerland/Users, the OU's advanced security settings show two new entries for that group: Reset Password and Read all properties, applying to user objects below the OU.
This is least privilege in practice. A helpdesk member cannot create admins, change group memberships or touch other sites' users. If a helpdesk account is phished, the attacker can reset passwords in one OU, which is bad, but far from owning the domain.
(To see the Security tab on AD objects, Advanced Features must be enabled in the console's View menu.)
Go deeper:
 Microsoft Learn: Delegation of Control wizard — common delegated tasks and custom tasks.