What do the IEC 62443 security levels SL 0 to SL 4 mean, and what are they used for?
They grade how strong an attacker a component must withstand, from no protection (SL 0) up to a sophisticated, well-resourced, highly motivated attacker with IACS-specific knowledge (SL 4). They are used to tailor the IEC 62443-4-2 component controls.
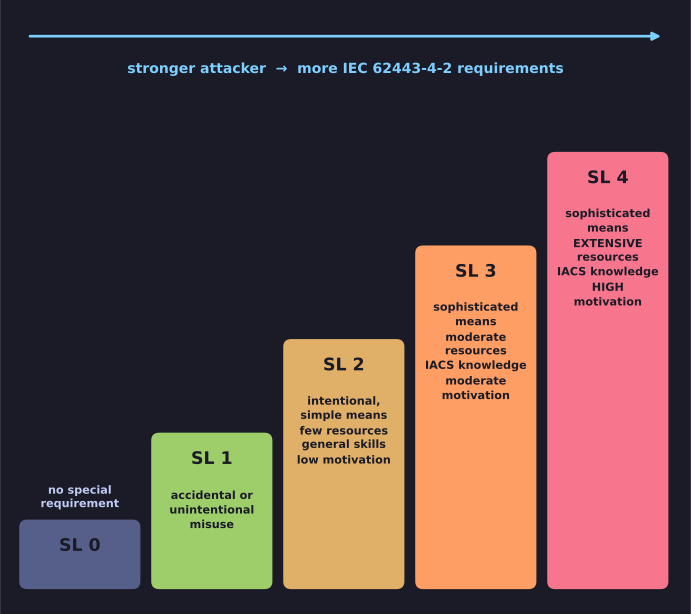
* Each security level is defined by the attacker it must hold off. *
IEC 62443 is the security standard for industrial automation and control systems (IACS). Each level is defined by the attacker it holds off, not by a list of features:
| Level | Protects against |
|---|---|
| SL 0 | No special requirement |
| SL 1 | Unintentional or accidental misuse |
| SL 2 | Intentional misuse by simple means: few resources, general skills, low motivation |
| SL 3 | Sophisticated means, moderate resources, IACS-specific knowledge, moderate motivation |
| SL 4 | Sophisticated means, extensive resources, IACS-specific knowledge, high motivation |
The SL is set per component or product. It then decides which requirements of part 4-2 apply. Higher levels add requirement enhancements, for example hardware-backed key storage. The jump from SL 1 to SL 2 is the jump from accidents to deliberate attackers. From SL 3 upwards the attacker knows industrial systems specifically.
Go deeper:
 ISA — ISA/IEC 62443 series of standards — the standards body page with the part structure
- IEC 62443 (Wikipedia) — overview of all parts, security levels and maturity levels