Quiz Entry - updated: 2026.10.13
What are the key CRA requirements for manufacturers?
A risk-based approach; no known exploitable vulnerabilities at release; secure by design and by default; security testing and vulnerability management with free security updates for a support period of at least five years; and reporting of actively exploited vulnerabilities to ENISA and the national CSIRT within 24 hours.
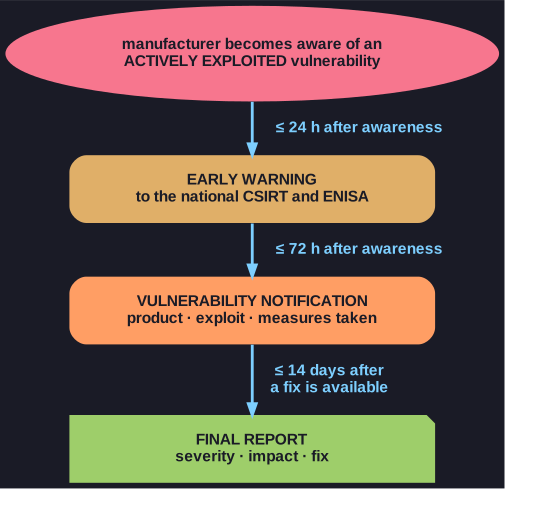
* Both early deadlines run from the moment the manufacturer becomes aware. *
- Risk-based: the manufacturer assesses the product's cybersecurity risks and designs for them.
- No known exploitable vulnerabilities when the product is placed on the market.
- Secure by design and secure by default: for example no default passwords and a minimal attack surface. Secure settings must be the shipped state.
- Vulnerability handling over a support period of at least five years (shorter only if the product is expected to be used for less time), with security updates provided free of charge.
- Reporting: an actively exploited vulnerability or a severe incident must be reported to ENISA and the national CSIRT. That means an early warning within 24 hours, a fuller notification within 72 hours, and a final report later.
The conformity assessment always needs one thing, whatever the category: the manufacturer must justify why each essential requirement is fulfilled. That justification is the technical documentation behind the CE mark.
Go deeper:
 European Commission — CRA implementation FAQ — official answers on support periods, reporting and the essential requirements