What are the goal, steps and deliverables of the threat analysis and risk assessment phase?
Identify and mitigate the security risks in the product design proactively, and keep residual risk acceptable. It delivers a threat model, a risk assessment, a mitigation plan, and the acceptance and monitoring of residual risks.
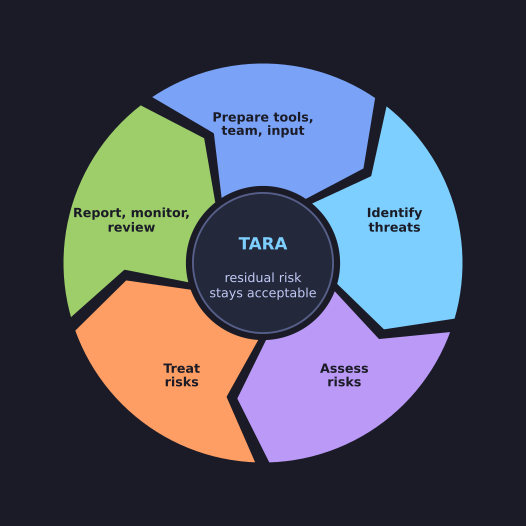
* Step five feeds back into step two: a threat model is reviewed for the whole product life. *
Product Security is responsible here. It needs a risk team, a methodology and rating scheme, risk catalogues and threat modelling or risk management tools.
- Prepare tools, team and input (architecture, requirements).
- Identify threats, for example with STRIDE over a data flow diagram.
- Assess risks: likelihood and impact, per the rating scheme.
- Treat risks: mitigate, avoid, transfer or accept.
- Report, monitor and regularly review them.
Step 5 makes it a loop. A threat model is not finished at design time. New vulnerabilities, features and attack techniques change the ratings, so the risk register is reviewed for as long as the product is in the field.
Go deeper:
 OWASP — Threat Modeling — the four-question method and links to tools
- STRIDE model (Wikipedia) — the threat categories used in step two