If business-critical websites stay blocked by a web proxy, how will users react, and what should the company do instead?
Users will find workarounds, each bringing new risks: internet via a phone hotspot, calling the site by IP address without DNS, an anonymising VPN, another proxy, or simply a private PC. The introduction and further operation of a content-control proxy must always come with support processes; here the administrator should, after a short check, add the sites to an exception list or release the whole category.
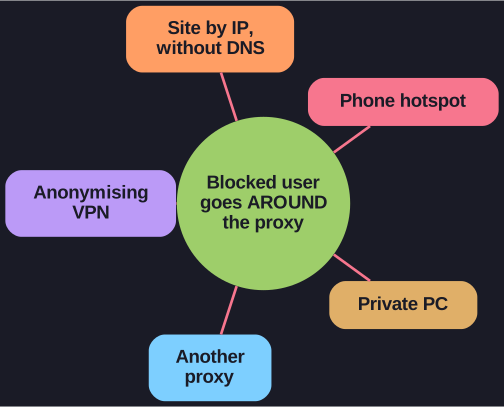
* Every workaround takes traffic around the control, so the company sees and protects less than before. *
Every one of these workarounds takes traffic around the control instead of through it, so the company ends up with less protection than before the proxy, plus traffic it can no longer see. This is the operational side of the gateway rule "all traffic must pass through it": people only keep routing through a control they can live with.
Tip: a security measure that blocks the business is not neutral; it pushes users toward shadow IT.
Go deeper:
 Shadow IT — Wikipedia — what users build when official IT blocks their work.
- Internet filter (content-control software) — Wikipedia — category lists, blacklists and their side effects.