How does the financial institution respond to the SAP router finding?
It reviews the gateway's configuration and decides to reduce its use to a minimum. An SAP administrator works out a suitable configuration together with a network security specialist, and the SAP router is additionally placed behind a restrictively configured firewall.
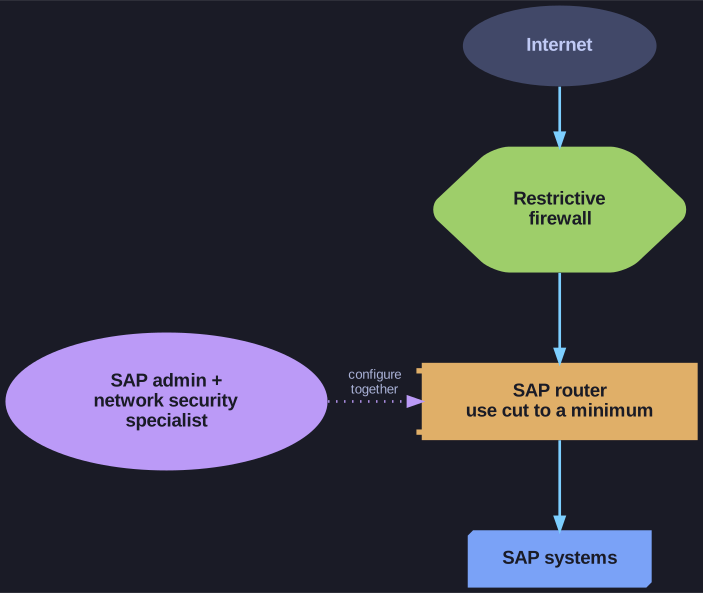
* Fewer uses, a firewall in front, and a configuration worked out by both specialists. *
Three ideas from the gateway topic meet here. First, inventory: a gateway that nobody lists as critical cannot be maintained or monitored as one. Second, minimise: every extra use (consultants, partners) is another opening, so drop what isn't needed. Third, gateways are not security solutions per se and need upstream protection, here a restrictive firewall in front. The pairing of an application specialist with a network specialist is deliberate: the router's rules only make sense with knowledge of both the SAP side and the network side.
Go deeper:
 SAP Support — SAProuter — the vendor's own page on the component, its purpose and setup.
- MITRE ATT&CK T1133 — External Remote Services — remote-access gateways as an attacker's way in.