How does a client authenticate to the Cisco DNA Center (Catalyst Center) REST API?
It sends an HTTP POST with Basic Authentication (username and password) to the token API, /api/system/v1/auth/token. A 200 response returns a token that authenticates all further API calls.
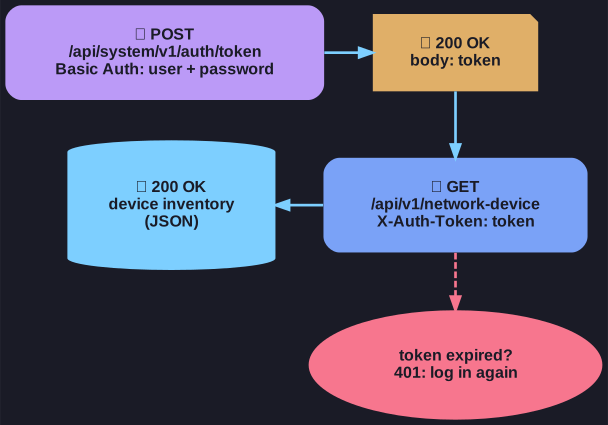
* Log in once with Basic Auth to get a token, then send the token instead of the password on every call; an expired token gives 401. *
Cisco DNA Center, now renamed Cisco Catalyst Center, expects all incoming REST data in JSON. Logging in works like this (shown in Bruno against Cisco's public DevNet sandbox):
- URL:
https://sandboxdnac.cisco.com/api/system/v1/auth/token - Method: POST.
- Authorization: type Basic Auth, with the sandbox username and password.
- Header:
Content-Type: application/json. - Send. A status of 200 means success, and the response body contains the token.
Basic Auth sends the credentials only once, to get the token. After that the client sends the token instead of the password on every call, which limits how often the password travels over the network. The token also expires after a while.
Go deeper:
 Cisco Catalyst Center API documentation — authentication, token validity and the API reference.
- Basic access authentication — Wikipedia — how username and password travel in the Authorization header.